Connect accounts to people and tasks
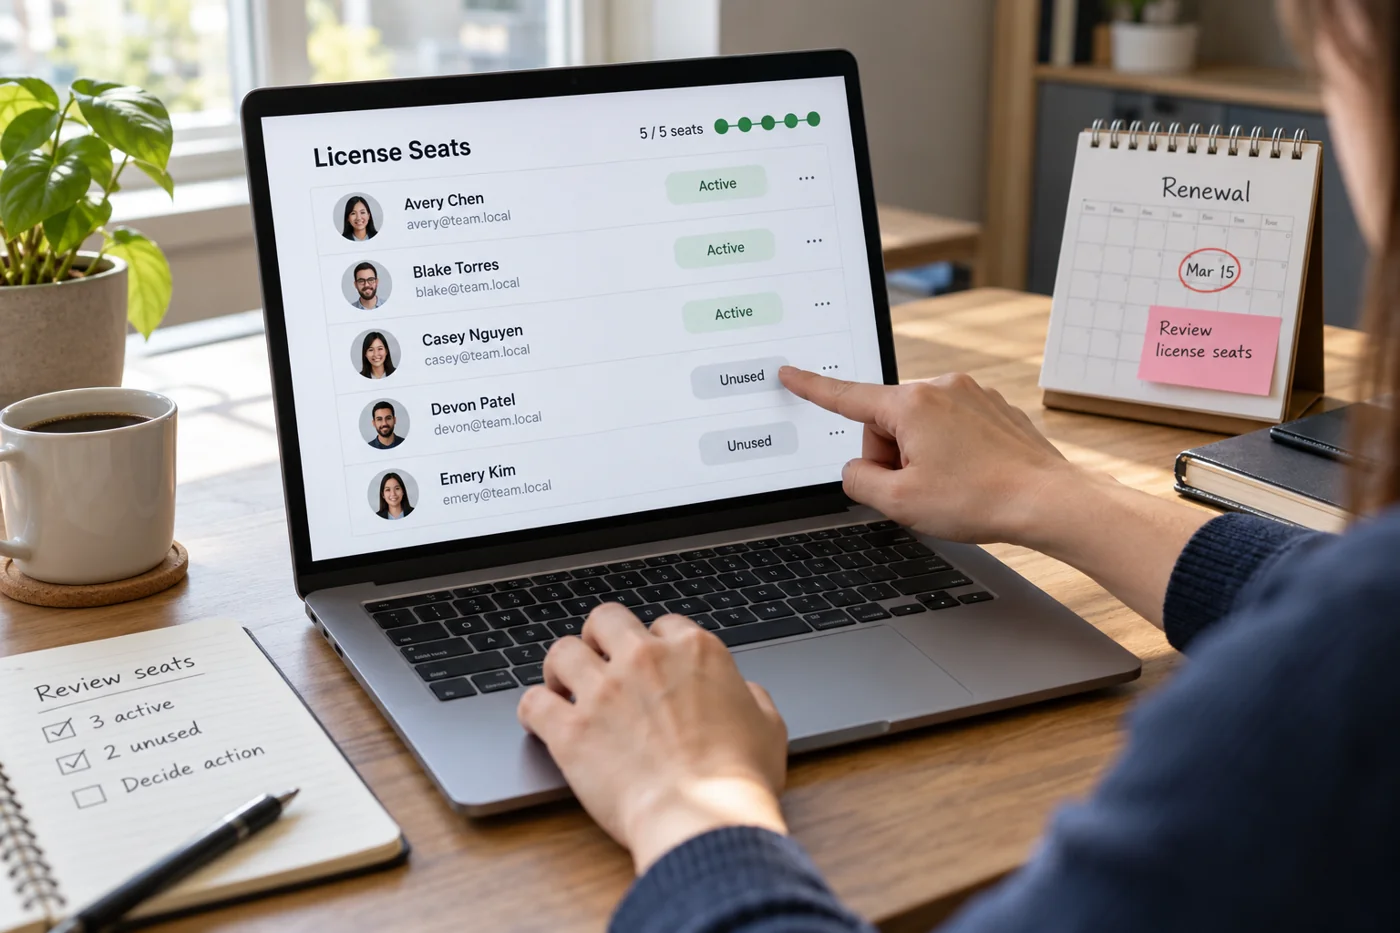
Compare the user list with the people who currently need access. Mark unknown names, duplicate accounts and people no longer responsible. Treat available activity information as a clue only. An infrequent login does not prove an account is unnecessary.
Ask about the particular purpose in unclear cases. A monthly export or cover arrangement can explain occasional use. Record the answer briefly so the same question does not recur at every renewal.
Check the effects of removal
An account may own files, automations or shared areas. Establish what happens to those components before removing access. Transfer options differ between products. Check current publisher guidance for the particular account.
Separate access decisions from paid-seat decisions. Depending on the agreement, changes may take effect at different times. Do not assume immediate refunds or automatic reductions in cost.
Carry out changes traceably
Create a short list of seats to retain, clarify or change. Have the responsible person review the proposed changes. Comparing the next bill afterwards shows whether the expected adjustment actually happened.
After a change, test the affected workflows. Can remaining people still reach necessary files? Does a shared task continue under the intended owner? Successfully removing a user does not establish that handover is complete.
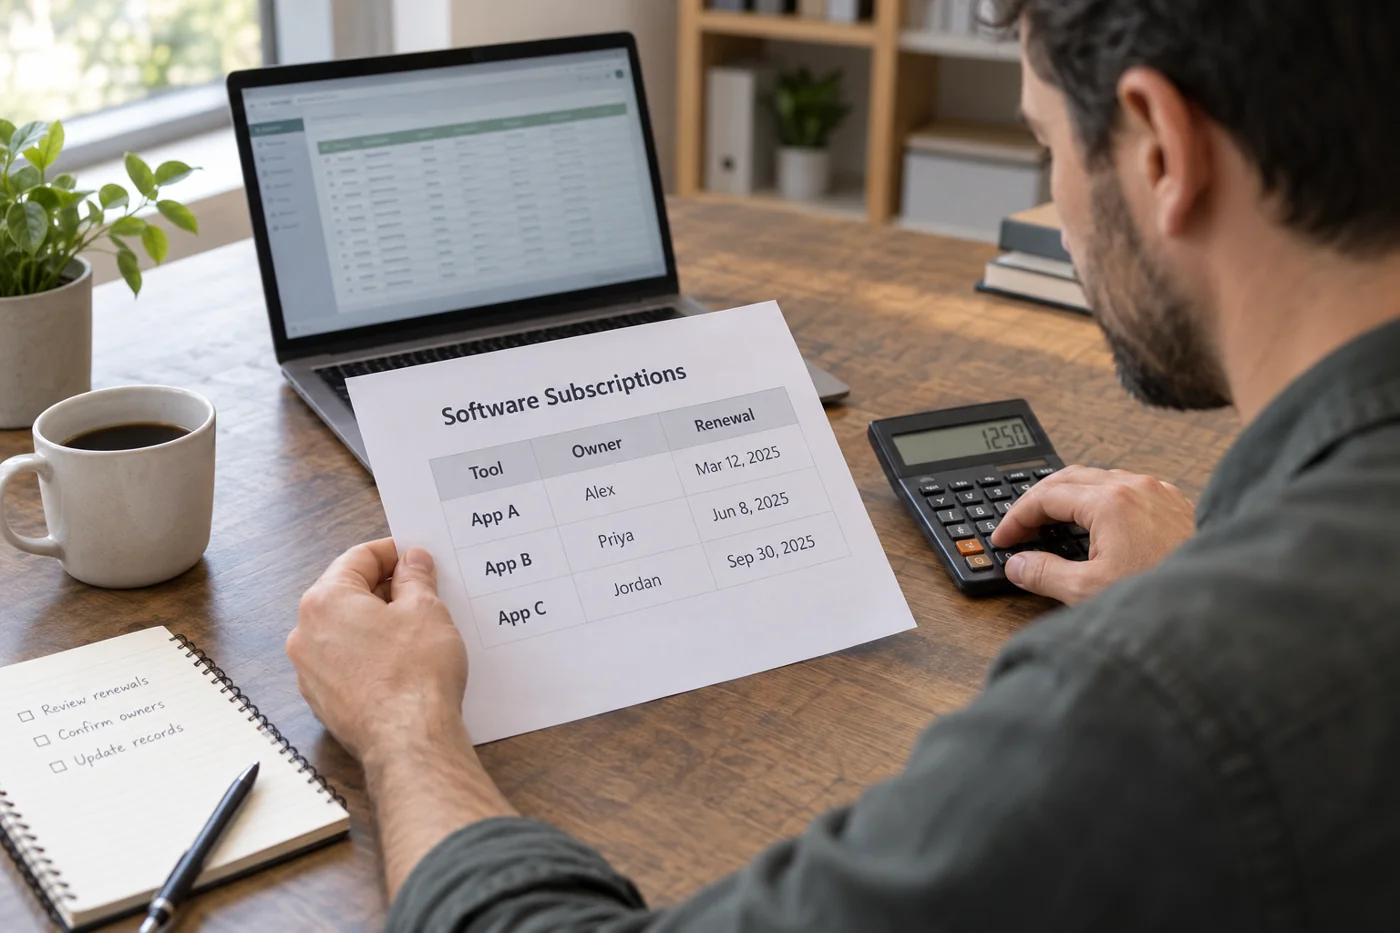
Record the decision and timing in the subscription inventory. This makes the next review easier. The goal is an appropriate number of managed accesses, not the smallest possible number regardless of consequences.
Check temporary cover arrangements as well. A seat may be needed during an absence without belonging permanently to another person. Record the intended duration and a later review date so temporary access does not become an unexplained permanent allocation.