Map accounts to responsibility
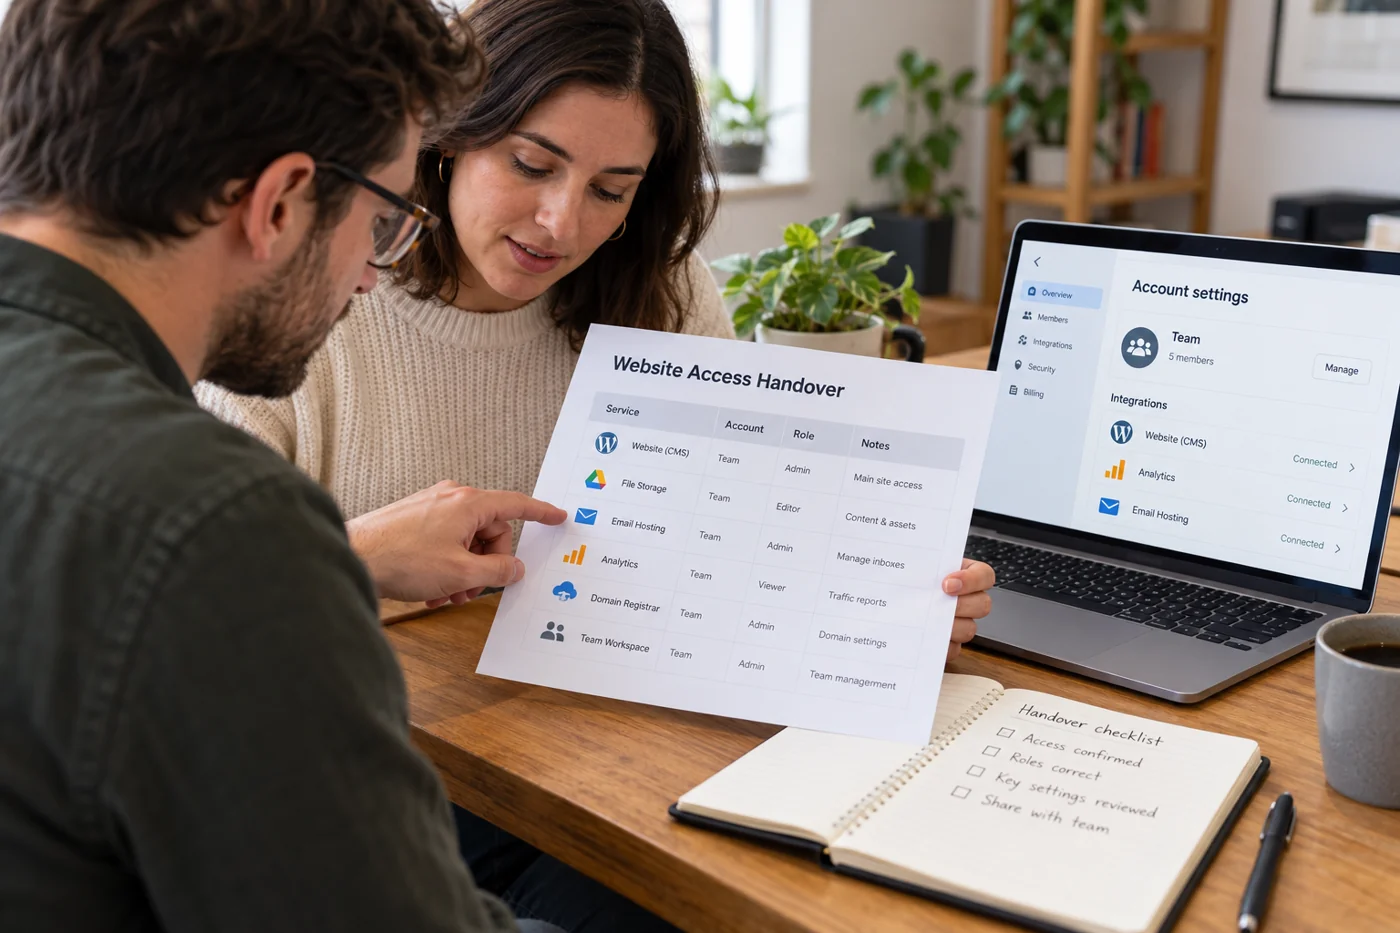
Create an overview of system, purpose, responsible role and intended access route. Do not turn it into an unprotected password collection. Use the designated secure management process and record only how authorized people obtain the necessary information. Knowing a username does not establish working access.
Check which accounts belong to individuals and which to the organization. A former maintainer's private email address may create a dependency for recovery or notifications. Establish the permitted change through the relevant system. Do not simply transfer someone's personal identity when an individual account with suitable permissions can be created.
Actually perform the required tasks
Have the receiving person use their intended account to check an ordinary task, such as opening a draft or finding an existing backup. Login alone does not confirm all required permissions. Use a harmless test and avoid altering production content merely to demonstrate access.
Check recovery and confirmation routes too. If another factor or approval is required, the responsible person needs to understand it. A handover requiring the former maintainer's last-minute help every time is not yet independently usable.
Include configuration and outstanding work
Add important dependencies: form sending service, backup procedure, publication process and known special cases. Describe unresolved problems and recent changes too. Working access is of limited help when nobody knows why part of the site is deliberately configured differently.
Link existing documentation and verify its availability through the new access. Instructions inside an inaccessible personal folder have not genuinely been handed over. With several providers involved, clarify who handles each area.
End old access in an organized way
Remove or reduce unnecessary permissions after confirmed handover through the intended procedure. First check whether automated processes or ownership roles depend on them. Premature deletion may create new problems, while indefinitely retained access also leaves responsibility unresolved.
Finally record which tasks were actually checked through the new account and which dependencies remain. Handover is not a one-time delivery of credentials, but a traceable transfer of responsibility and usable permissions.